
Why Cloud Resources Keep Growing
Monday morning, your finance lead sends a message. The cloud bill jumped again, and she wants to know why. You open the console and scroll through hundreds of resources. You…
Read article →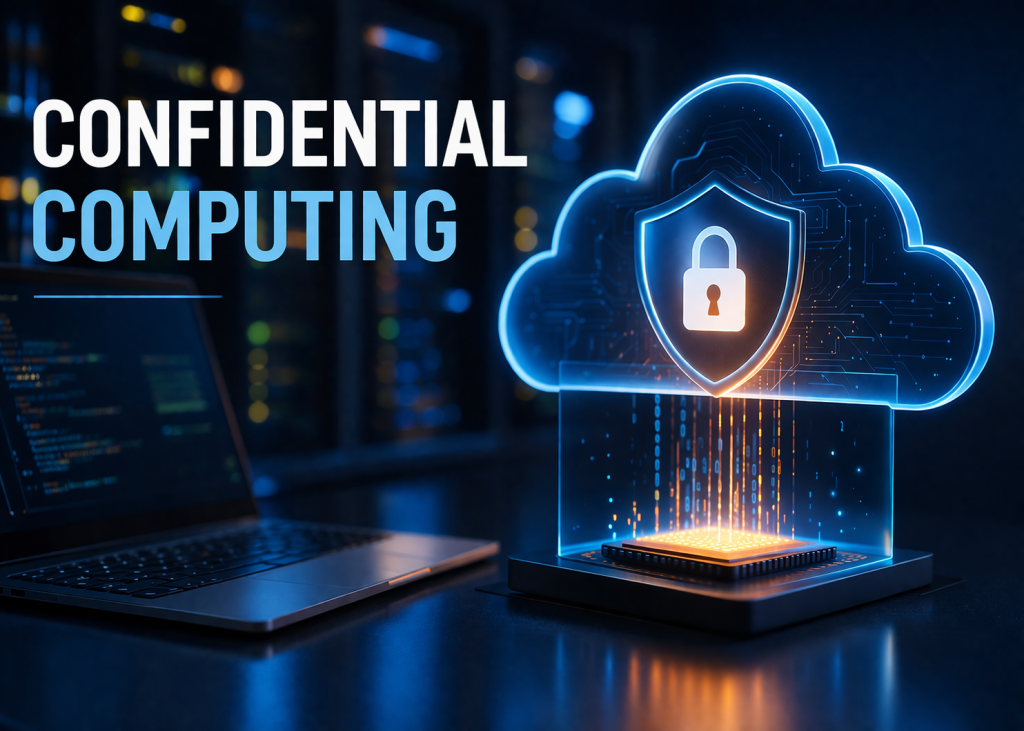
Cloud security has really evolved over the years. Nowadays, encryption for data at rest and in transit is pretty much standard practice in modern architectures. However, there’s always been that one vulnerable moment—when data is actively being processed. That’s where the discussion about confidential computing kicks off.
For a long time, businesses accepted this limitation as just part of the cloud experience. But as digital ecosystems have become more intricate and data has grown more sensitive, that compromise has started to feel a bit too risky. Financial transactions, healthcare records, AI models, and proprietary algorithms aren’t just sitting there or being sent around—they’re constantly being utilized, analyzed, and transformed.
And that’s precisely where the demand for stronger protection comes into play.
Confidential computing isn’t just another layer of security; it represents a fundamental shift in how we perceive trust within cloud environments.
To understand the importance of confidential computing, it helps to look at the traditional security model.
Most cloud strategies are built around three states of data:
The first two states have been well-handled with encryption and secure protocols. But when data is being processed—whether it’s in memory or the CPU—it gets temporarily decrypted. This brief moment opens the door for potential exposure.
In simpler terms, even the most secure systems have had times when data was at risk.
A decade ago, this might not have raised too many alarms. But nowadays, organizations are:
The stakes have never been higher, and the appetite for risk has drastically diminished. Confidential computing bridges this gap by ensuring that data stays encrypted, even while it’s being processed.
At its core, confidential computing leverages hardware-based security methods—commonly known as Trusted Execution Environments (TEEs)—to safeguard and isolate data while it’s being processed
Imagine it as a secure little fortress nestled within the cloud infrastructure. Even if someone has access to the larger system, they won’t be able to peek inside that protected space. This fundamentally alters the trust model.
Instead of relying solely on perimeter security or access controls, organizations can now ensure that:
It is a subtle shift, but a powerful one.
Not every workload needs confidential computing, but for certain industries and specific use cases, it’s becoming a must-have.
Banks and fintech firms handle extremely sensitive transactional data. Systems for fraud detection, risk modeling, and payment processing all gain from keeping data secure while it’s being used.
Patient records, diagnostic information, and research datasets demand strict privacy measures. Confidential computing allows for secure collaboration without revealing raw data.
Training models on sensitive information can pose privacy risks. With confidential computing, organizations can train and operate models without exposing the underlying datasets.
In situations where several organizations need to collaborate on shared data—without fully trusting one another—this technology plays a crucial role.
It is tempting to view confidential computing as just another feature offered by cloud platforms. But in practice, it requires a more thoughtful approach.
Implementing it successfully involves:
This is where many organizations hesitate.
Not because the technology is not valuable, but because it is not straightforward.
This is where the role of managed cloud services becomes much more than operational support.
Confidential computing sits at a layer where infrastructure, security, and application design intersect. It requires a clear understanding of:
Without the right expertise, organizations risk either underutilizing the technology or implementing it incorrectly.
A structured approach often looks like this:
It is not about applying the technology everywhere. It is about applying it where it matters most.
One of the key reasons this topic is really picking up steam is its connection to zero trust principles. The zero trust model operates on the idea that no system, user, or process should be taken at face value. Every interaction needs to be verified.
Confidential computing takes this concept a step further by ensuring that data stays protected even while it’s being processed. Essentially, it eliminates the need to fully trust the environment. This is especially important in situations like:
This is particularly valuable in:
It provides an extra layer of assurance that traditional security models simply can’t match on their own.
Even though it has a lot of potential, many organizations are still in the early stages of adopting this technology. Here are some common hurdles they face:
It’s not always easy to figure out when and how to use confidential computing.
Current applications might need some tweaks to work within secure enclaves.
While things are improving quickly, there can still be some trade-offs based on the workload.
Many teams lack hands-on experience with this relatively new approach.
These challenges are definitely real, but they shouldn’t be seen as barriers—instead, they highlight the need for a more guided approach.
As cloud environments grow more sophisticated, the expectations from providers are changing.
It is no longer enough to:
Organizations now expect support in:
This is where cloud management services are evolving.
They’re becoming more proactive, strategic, and closely aligned with business outcomes. Confidential computing fits right into this evolution because it demands ongoing oversight and adaptation. It’s not just a one-time setup; it’s a continuous capability that evolves over time.
It’s interesting to note that many organizations aren’t just diving into confidential computing on its own. Instead, it often plays a role in a larger modernization journey. When businesses transition to the cloud, they take a fresh look at several key areas:
– how applications are developed
– data moves between systems
– security measures are implemented
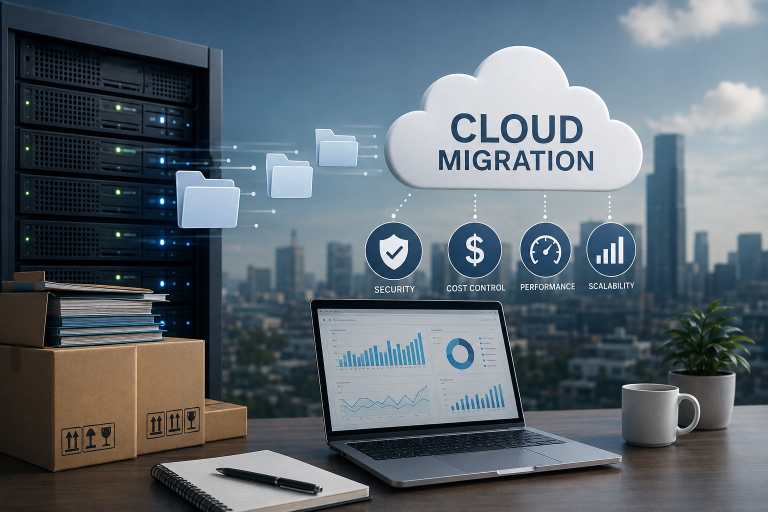
This presents a great chance to weave in stronger security practices right from the start. In this light,cloud migration services have evolved beyond simply shifting workloads from one place to another. They now focus on redesigning systems to be more secure, scalable, and ready for the future. Confidential computing becomes a crucial piece of that transformation puzzle.
For organizations considering this approach, it helps to start small. Instead of trying to apply confidential computing across the entire environment:
This phased approach reduces risk and builds confidence.
At the same time, having the right expertise in place ensures that each step is aligned with long-term goals.
We are moving toward a world where:
In such a landscape, traditional security models feel incomplete.
Confidential computing introduces a new baseline—one where data does not need to be exposed, even temporarily, to be useful.
It shifts the focus from protecting systems to protecting the data itself, at every stage.
Cloud security has evolved beyond just keeping threats at bay. Now, it’s all about making sure that even in the most intricate and ever-changing environments, sensitive data stays safe.
Confidential computing is a significant leap in that direction.
For organizations, the real question isn’t whether to embrace it, but rather how to integrate it in a way that fits their architecture, compliance requirements, and business goals. This is where a smart mix of strategy and execution becomes crucial.
While the technology itself is impressive, its true worth lies in how carefully it’s put into practice and managed.
As cloud environments keep changing, approaches like this will shape the future of secure, intelligent, and resilient digital systems.
Monday morning, your finance lead sends a message. The cloud bill jumped again, and she wants to know why. You open the console and scroll through hundreds of resources. You…
Read article →You dread deployment day. You flinch when the cloud invoice lands in your inbox. You’ve stopped trying to explain the architecture to new hires because you’re not fully sure how…
Read article →Your migration was supposed to be finished by now. Instead, you’re staring at a cloud bill that’s twice your budget. An application keeps timing out. Your team is exhausted from…
Read article →Tell us where you are and what's slowing you down. A senior engineer will get back to you within one business day.
Our team will get back to you within one business day.
Leave a Reply